Description (CNA)
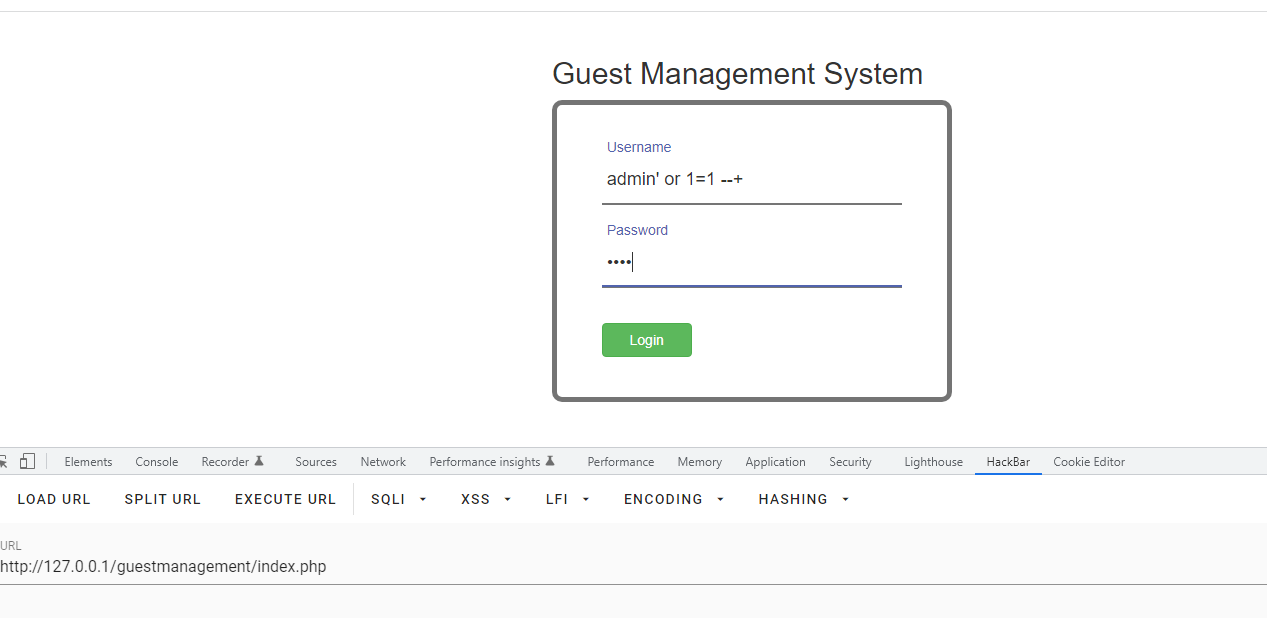
A vulnerability classified as critical was found in SourceCodester Guest Management System. This vulnerability affects unknown code of the file index.php. The manipulation of the argument username/pass leads to sql injection. The attack can be initiated remotely. The exploit has been disclosed to the public and may be used. VDB-206398 is the identifier assigned to this vulnerability.
Affected (CNA)
| Vendor / product | Versions |
|---|---|
| SourceCodester / Guest Management System | affected n/a |
CWE
CWE-89
References
ADP enrichment
No English description supplied.
No English description supplied.
No references supplied.