Description (CNA)
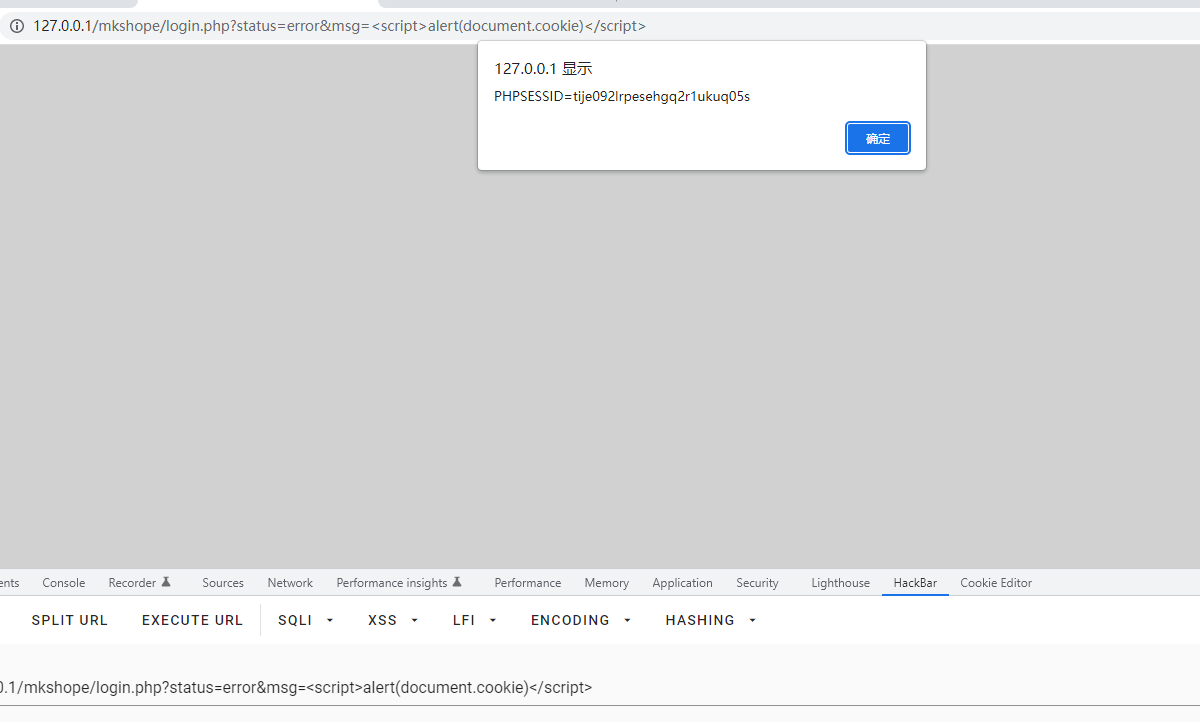
A vulnerability has been found in SourceCodester Simple and Nice Shopping Cart Script and classified as problematic. Affected by this vulnerability is an unknown functionality of the file /mkshope/login.php. The manipulation of the argument msg leads to cross site scripting. The attack can be launched remotely. The exploit has been disclosed to the public and may be used. The identifier VDB-206401 was assigned to this vulnerability.
Affected (CNA)
| Vendor / product | Versions |
|---|---|
| SourceCodester / Simple and Nice Shopping Cart Script | affected n/a |
CWE
CWE-79
References
ADP enrichment
No English description supplied.
No English description supplied.
No references supplied.