Description (CNA)
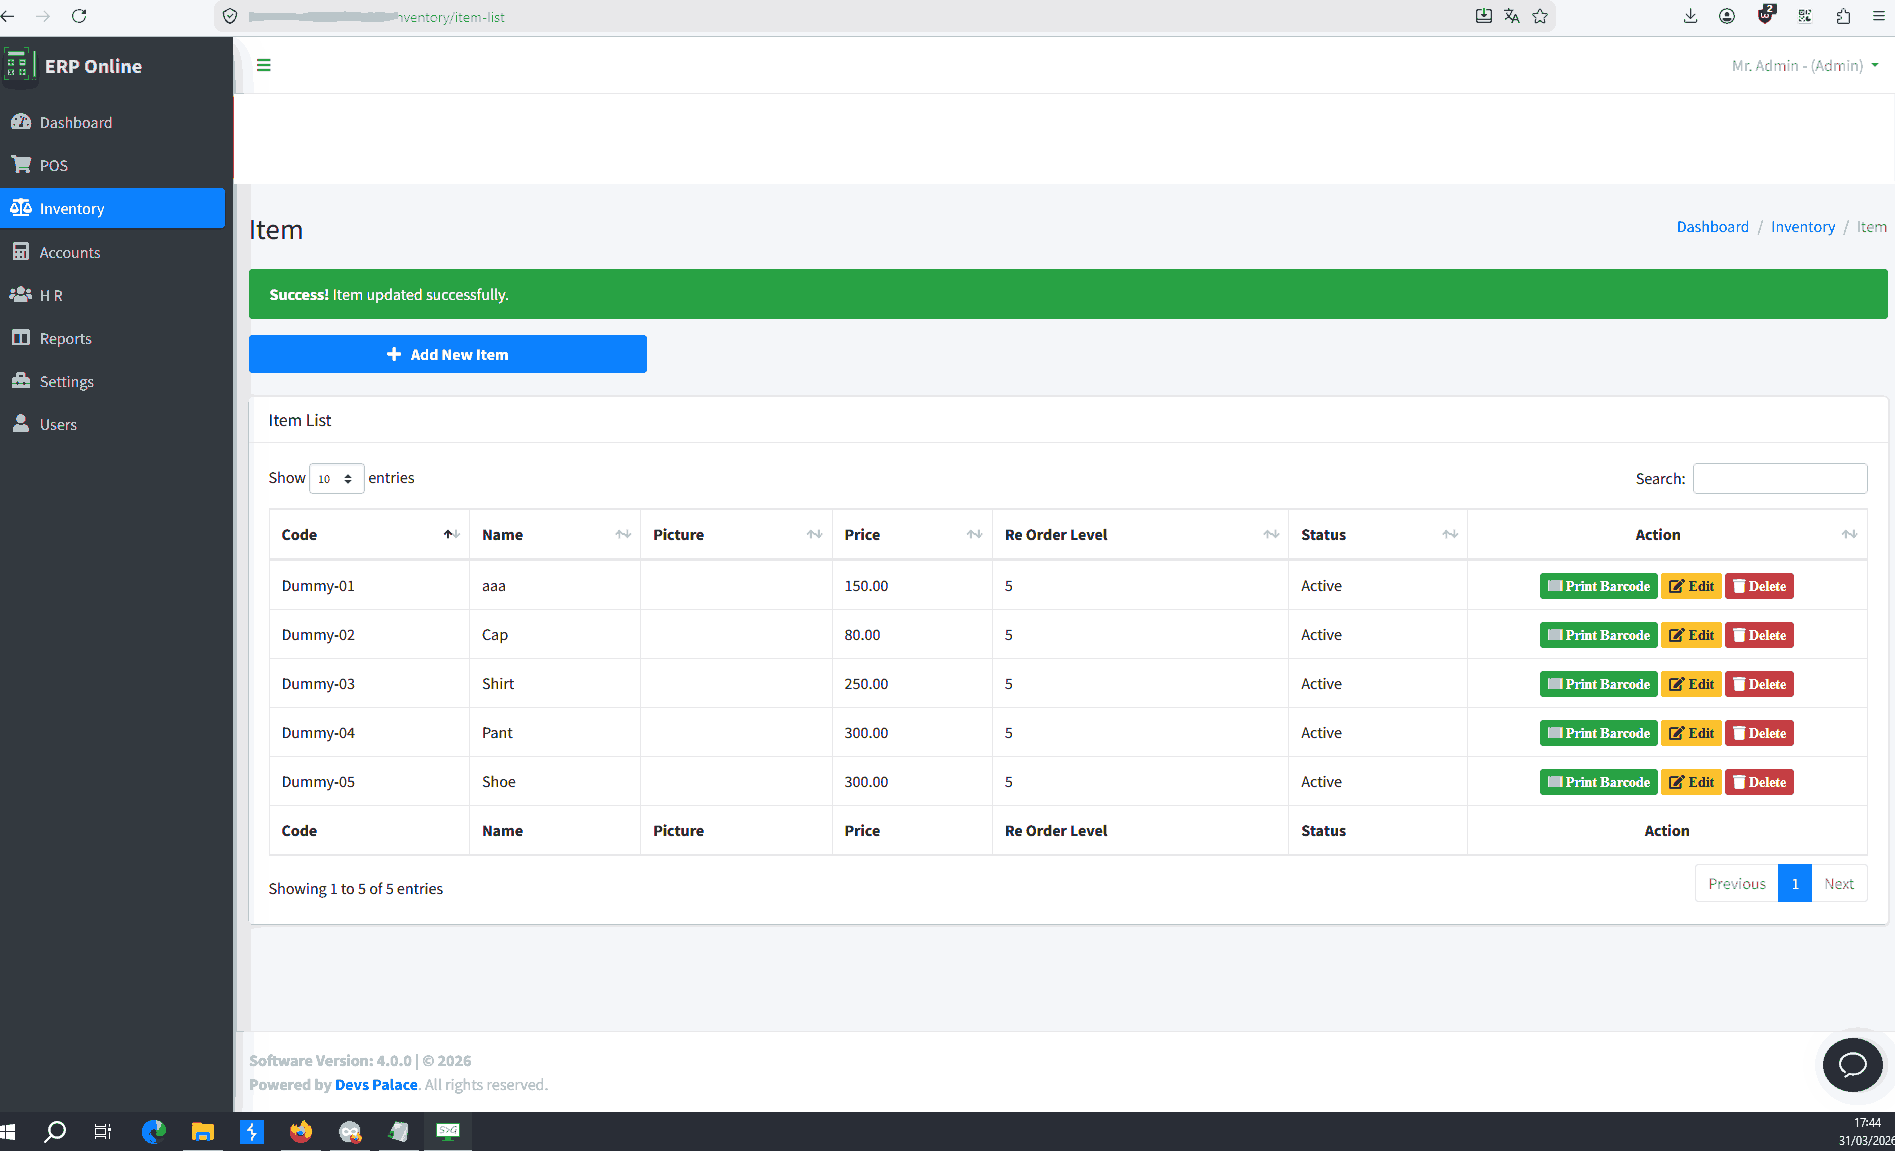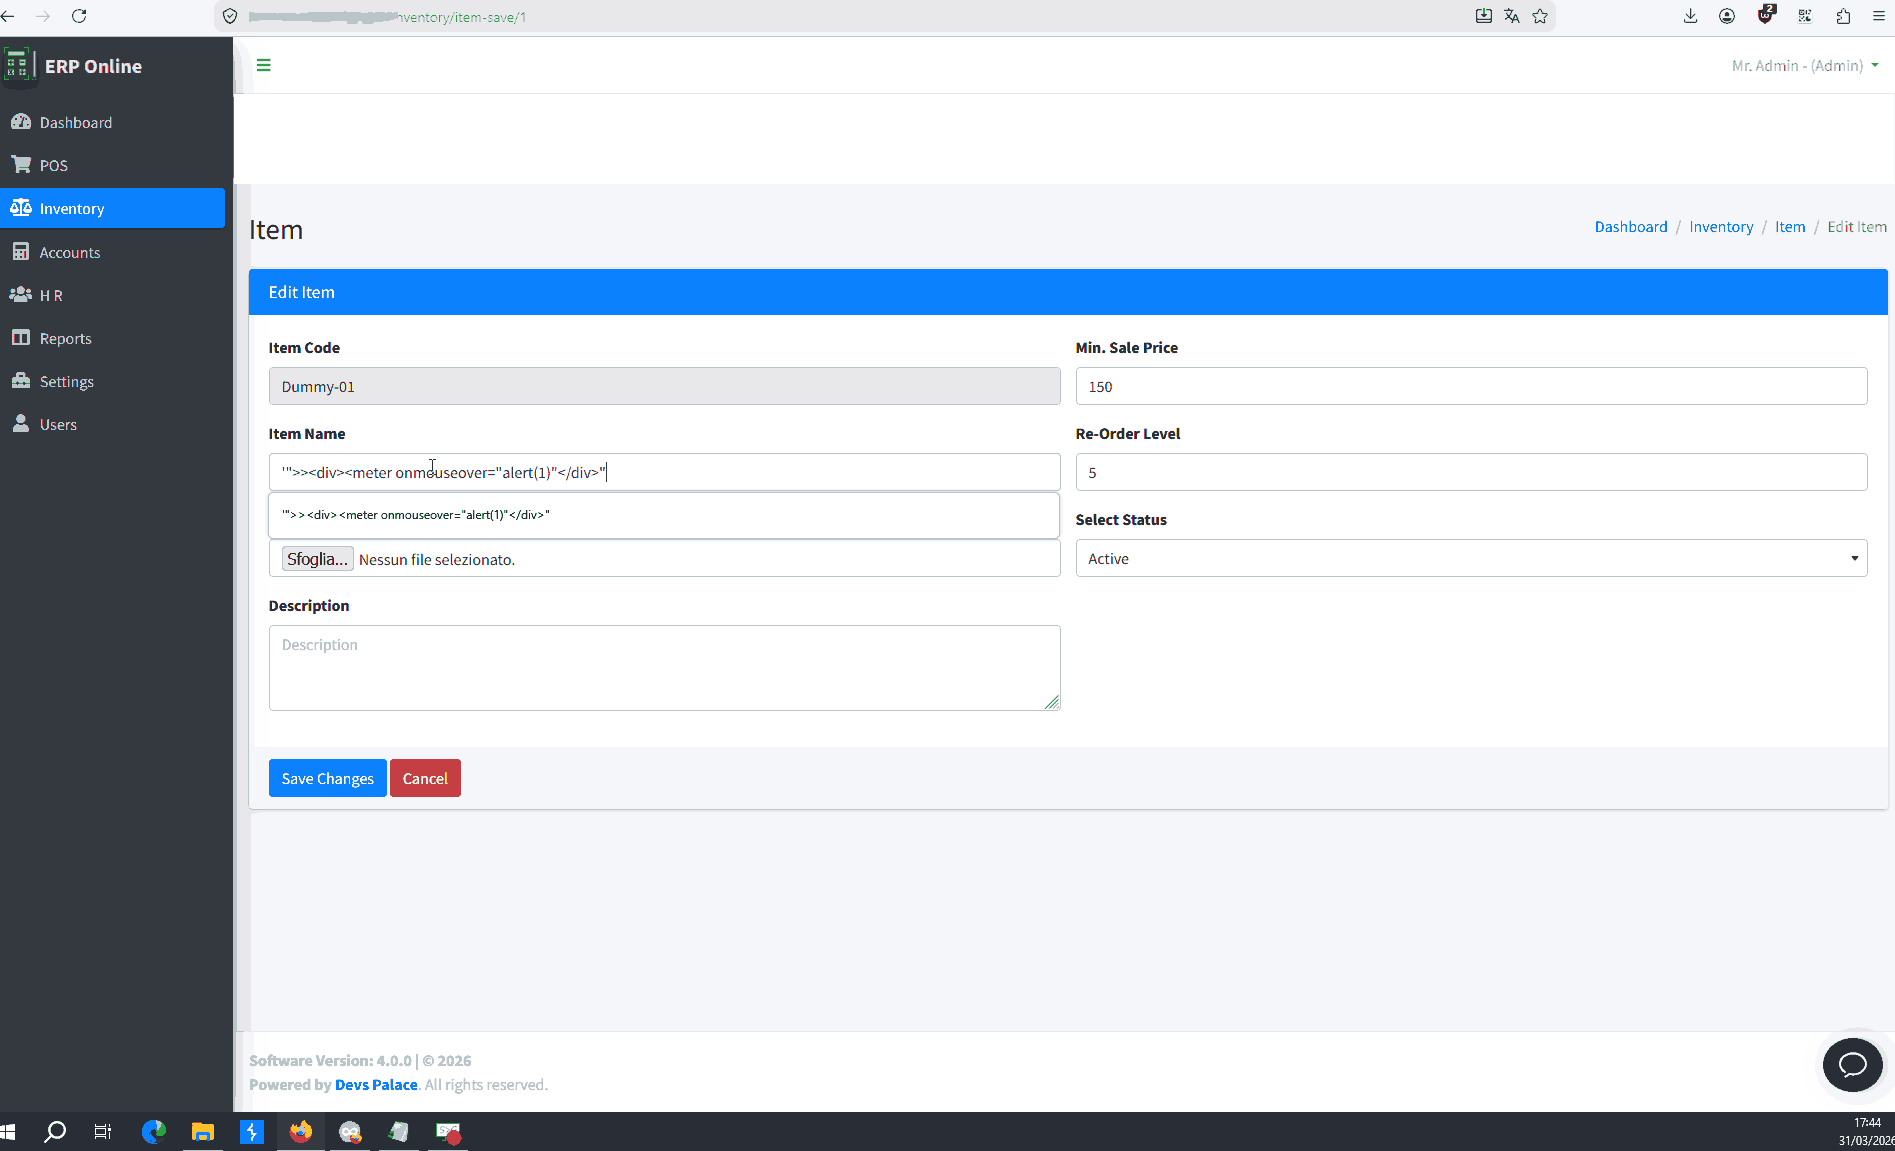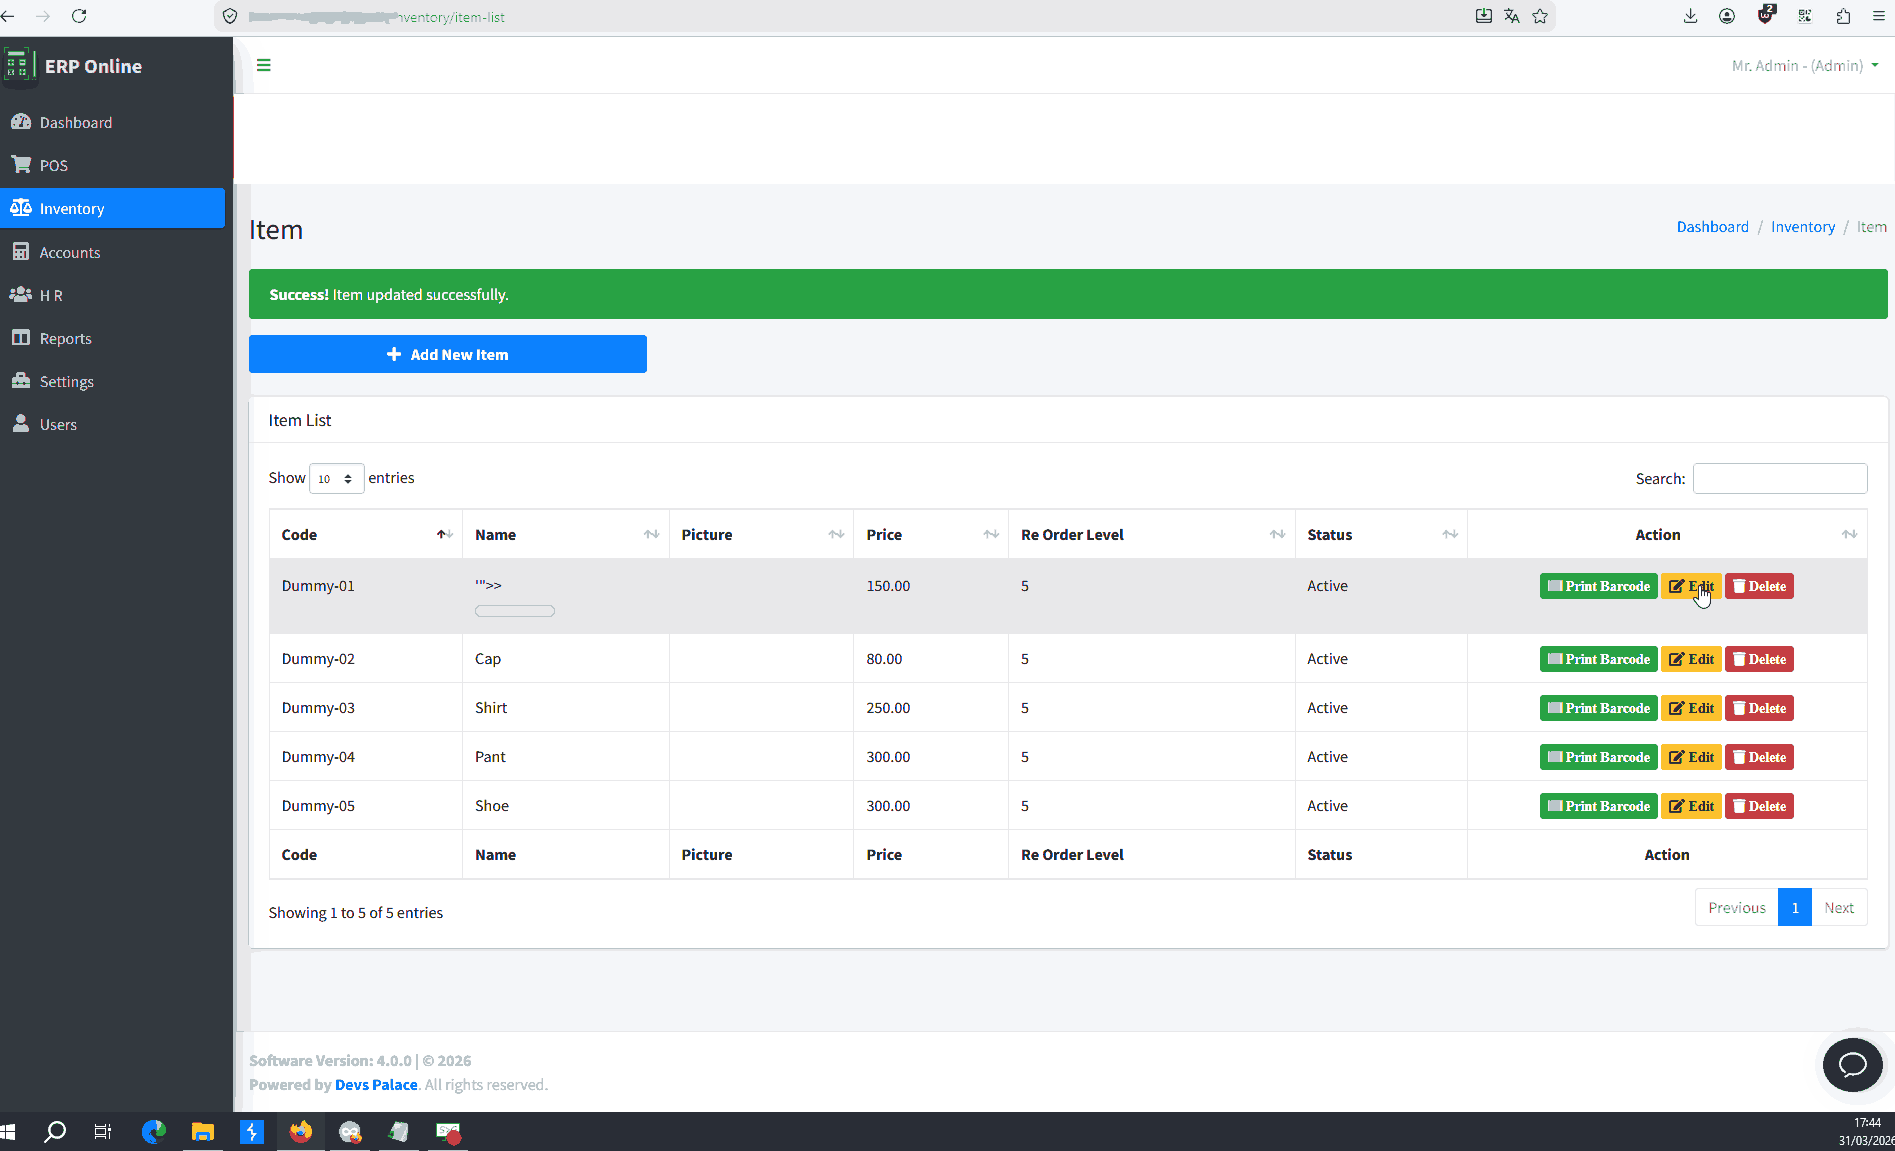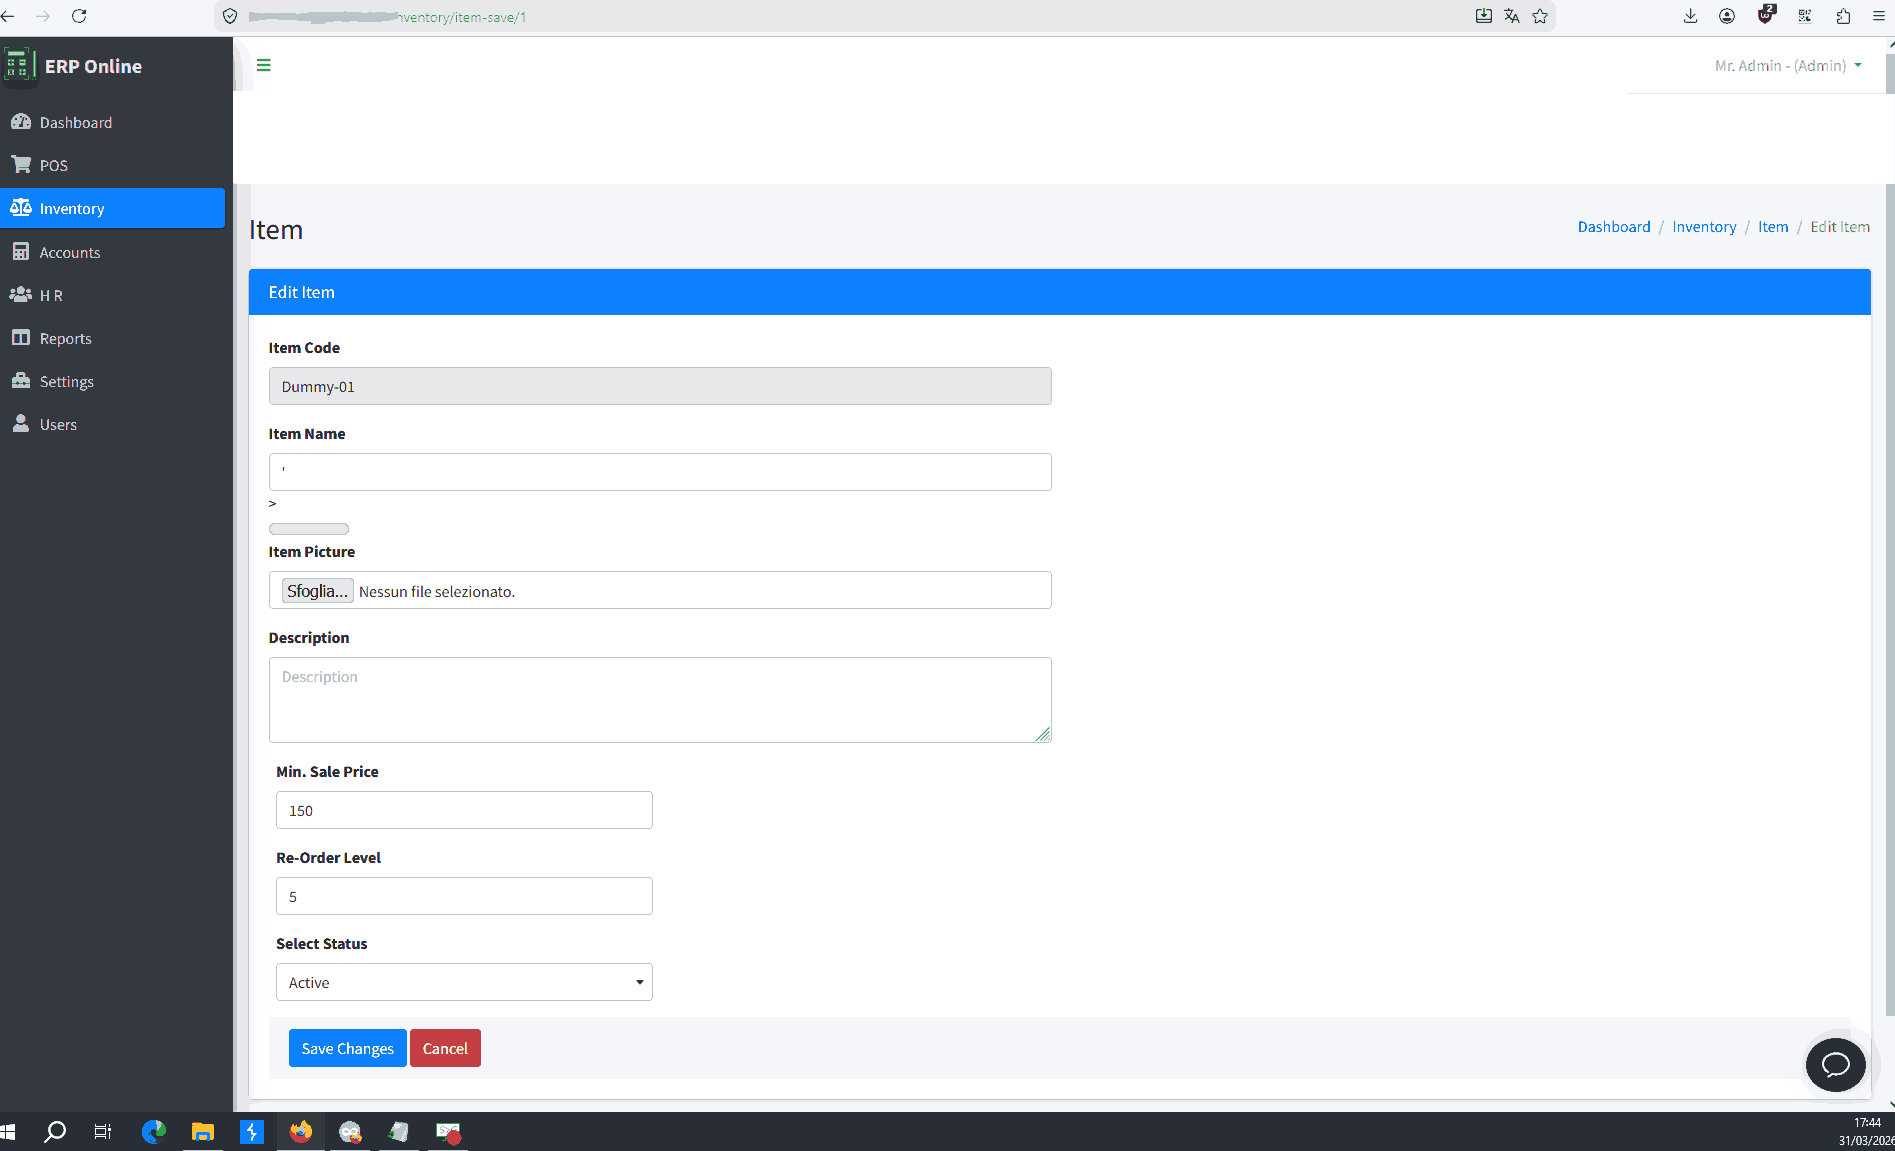
A vulnerability was identified in Devs Palace ERP Online up to 4.0.0. This impacts an unknown function of the file /accounts/chart-save. Such manipulation leads to cross site scripting. The attack may be performed from remote. The exploit is publicly available and might be used. The vendor was contacted early about this disclosure but did not respond in any way.
Affected (CNA)
| Vendor / product | Versions |
|---|---|
| Devs Palace / ERP Online | affected 4.0 |
CWE
CWE-79, CWE-94
References
- https://vuldb.com/vuln/362559
- https://vuldb.com/vuln/362559/cti
- https://vuldb.com/submit/809930
- https://olografix.org/acme/_poc/ERP_Online-POC1.gif
ADP enrichment
No English description supplied.
No references supplied.